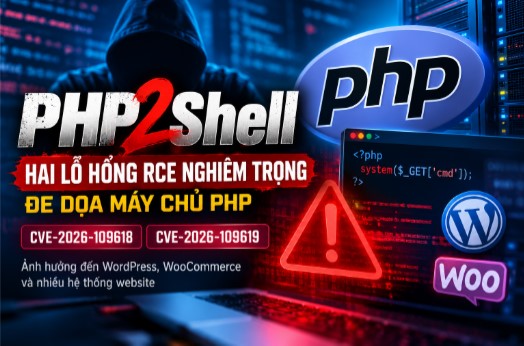

Two vulnerabilities carrying the identifiers CVE-2026-109618 and CVE-2026-109619 are rated as serious, PHP2Shell can affect Servers running PHP, including systems using WordPress, WooCommerce and e-commerce platforms.
📢 Join the channel Telegram belong to AnonyViet
Update new articles, cool tools and IT tips fastest
What’s worrying is that the problem lies with the PHP execution environment itself, rather than just a specific plugin or application. Therefore, installing additional security plugins or editing the website source code may not solve the risk.
What is PHP2Shell?
PHP2Shell is the name mentioned in information about the tool that exploits two new PHP RCE vulnerabilities. According to Sansec, images of an exploit tool called PHP2Shell were leaked along with information about the vulnerabilities.
RCE, short for Remote Code Execution, is a bug that allows attackers to execute code on a remote system when the necessary exploit conditions are met. If successfully exploited on PHP Server, the consequences can go far beyond taking over normal website administration.
Depending on how the Server is configured and the permissions of the PHP process, an attacker may attempt to read sensitive data, modify website files, install malicious code, create backdoors, or continue to penetrate deeper into the system.
For e-commerce websites, the risk is also related to customer data, order information and the ability to insert code to steal payment information.
Sansec said both vulnerabilities were rated CVSS v4.0 9.2/10, belonging to the very high severity group. However, the CVSS score does not mean that every Server is guaranteed to be successfully exploited; The actual level of risk depends on the version, configuration and access of the attacker.
What systems do the two vulnerabilities CVE-2026-109618 and CVE-2026-109619 affect?
According to initial information, these vulnerabilities have a wide range of effects on the PHP running environment.
Servers using PHP version 5.4 or higher may be affected. The leaked miner also claims to support multiple PHP versions, but the tool’s claim should not be interpreted as independent evidence that any version is exploitable in any configuration.
Systems that need to be tested include:
- WordPress websites, especially websites that use many PHP plugins.
- WooCommerce and online stores run on WordPress.
- Magento, Adobe Commerce and Shopware.
- Self-developed web applications using PHP.
- Systems that use Laravel, Drupal, Joomla or other PHP platforms, if the respective PHP environment is within the scope of influence.
For VPS Admin, this means checking all websites and PHP services on the Server, instead of just checking a website that is showing signs of abnormalities.
Why is installing Wordfence, a security plugin or a WAF safe enough?
If the vulnerability resides in PHP processing before the application code is executed, protection mechanisms operating at the application layer may not be able to prevent the entire exploit.
For example, Wordfence can help detect or block many forms of malicious traffic targeting WordPress. Cloudflare’s WAF can also help filter suspicious requests. However, the effectiveness of protection depends on the method of exploitation, the location of the protection layer and the ability to recognize attack patterns.
If a malicious request gets past the filtering layers and triggers errors within PHP, the website could still be in danger.
Sansec also warns against waiting for a new protection rule from Sansec Shield before updating. Application layer mitigations cannot be considered an alternative to official PHP patches.
Important rule: When the vulnerability is in the PHP runtime, it should be handled at the PHP runtime. Security plugins and WAFs should only be viewed as additional layers of defense.
How to test and handle PHP2Shell on VPS
If you are managing a WordPress website or VPS using DirectAdmin, cPanel or another control panel, you should follow the steps below.
On Linux Server, you can check the PHP CLI version with the command:
php -v
This command displays the PHP version of the command line interface. However, the PHP CLI may be different from the version the website is using through PHP-FPM or Apache.
Therefore, Admin needs to further check the PHP version assigned to each website in the hosting control panel, PHP-FPM configuration and related services.
For WordPress, you can enter Tools → Site Health → Information → Server to see the PHP environment information that the website reports.
You should not just check one PHP version and conclude that the entire Server is safe, especially when the VPS is running many websites with different PHP versions.
PHP update commands to reduce PHP2Shell risk
Note: The commands below depend on your operating system and PHP installation. Before updating the active Server, back up your website, database, and configuration. The package update command does not guarantee that PHP has been patched if the vendor has not released a fix for the software repository in use.
1. Ubuntu/Debian: update PHP packages
If PHP was installed from the Ubuntu or Debian APT repository, log in to SSH with an account with sudo privileges and run:
sudo apt update
apt list --upgradable 2>/dev/null | grep -E 'php[0-9.-]*|php[0-9]'
sudo apt upgrade
Command apt update refresh package list; apt upgrade Update packages that have upgrades in the configured repository. If you want to update PHP packages separately, specify the correct package name first. The example below is only relevant if these packages are installed and the software repository offers updates:
sudo apt install --only-upgrade php8.3-cli php8.3-fpm php8.3-common
Replace 8.3 with the actual version. On Ubuntu/Debian, security patches can be provided to the current PHP branch without changing the major version number. Check your distribution’s security notice.
2. DirectAdmin: check and update via CustomBuild
If the VPS uses DirectAdmin with CustomBuild, it should not be assumed to run apt upgrade is enough. PHP can be compiled and managed separately through CustomBuild.
cd /usr/local/directadmin/custombuild
./build update
./build versions
./build options
The above commands help update CustomBuild information and check software version/configuration. ./build update_versions Update software version information that CustomBuild manages; This command does not mean that PHP has been upgraded or patched.
./build update_versions
./build versions
After confirming the patch is available, update the correct PHP branch according to the CustomBuild configuration and DirectAdmin documentation. Do not arbitrarily change the PHP version without checking compatibility with the theme, plugins and website source code.
Reference: Documentation of service upgrade using DirectAdmin CustomBuild.
3. AlmaLinux/Rocky Linux/CentOS: update via DNF or YUM
If PHP is installed from the operating system’s RPM repository, it can be checked and updated using DNF:
sudo dnf check-update
sudo dnf upgrade 'php*'
On old systems using YUM:
sudo yum check-update
sudo yum update 'php*'
Warning: Use these commands only when PHP is managed using RPM from configured repositories. If the Server uses DirectAdmin CustomBuild or a third-party PHP repository, identify the correct package source to avoid conflicts.
4. Check the PHP version and running service
After updating, check PHP CLI and PHP-FPM services:
php -v
systemctl --type=service --state=running | grep php
If you need to restart PHP-FPM, use the correct service name on the Server. For example:
sudo systemctl restart php8.3-fpm
Replace php8.3-fpm by the actual service name. Do not run the example command if the Server is not using that service. Version shown in php -v It may be different from the version the website runs via PHP-FPM or Apache.
What should WordPress admins keep in mind?
With WordPress websites, two misconceptions need to be avoided: simply updating WordPress is enough, or simply installing a security plugin can handle all vulnerabilities.
WordPress, themes, plugins and PHP are different components in one system. A vulnerability in PHP may require patching at the Server layer, while WordPress and plugin updates are still needed to reduce other independent risks.
If you’re using WordPress on a private VPS, you should proactively manage your PHP version, monitor security alerts, and maintain a regular update process. If you use shared hosting or do not have Server administrator rights, please contact the provider to confirm when the patch will be applied.
In particular, you should not assume that the Server is safe just because the website is still accessible normally. Vulnerabilities can exist without causing obvious errors to the user.
Conclude
PHP2Shell is a notable security warning for the website administration community, especially WordPress, WooCommerce systems and e-commerce applications running on PHP.
Two vulnerabilities, CVE-2026-109618 and CVE-2026-109619, are rated by Sansec as serious, with a CVSS v4.0 score of 9.2/10. Since the described issue is at the PHP layer, the focus is to identify the affected environment and deploy the appropriate patch at the Server level.
If you are managing a VPS or a website that stores important data, check the PHP version, prepare a backup, contact the hosting provider when necessary and follow the official announcement from PHP. You should not wait until the website shows signs of being attacked before starting to handle it.